Penva Security

Preparing your security assessment

Loading your page…
Penva Security

Web Penetration Testing Services

Scope your penetration test

Secure submission

Giving you the Premium Security Experience

Essential Security
Premium Security
Meet Compliance and Audit Needs
Manual pentest approach following OWASP guideline
Pentest Report and Certificate
Aligned with Industry Standards (ISO 27001, SOC2, CREST, PCI DSS)
Continuation Collaboration
Fix issues during pentest and provide clean report at the end
In-depth Security Assessment
Every feature and endpoint is tested, prioritizing security above all
Transparency and Accountability
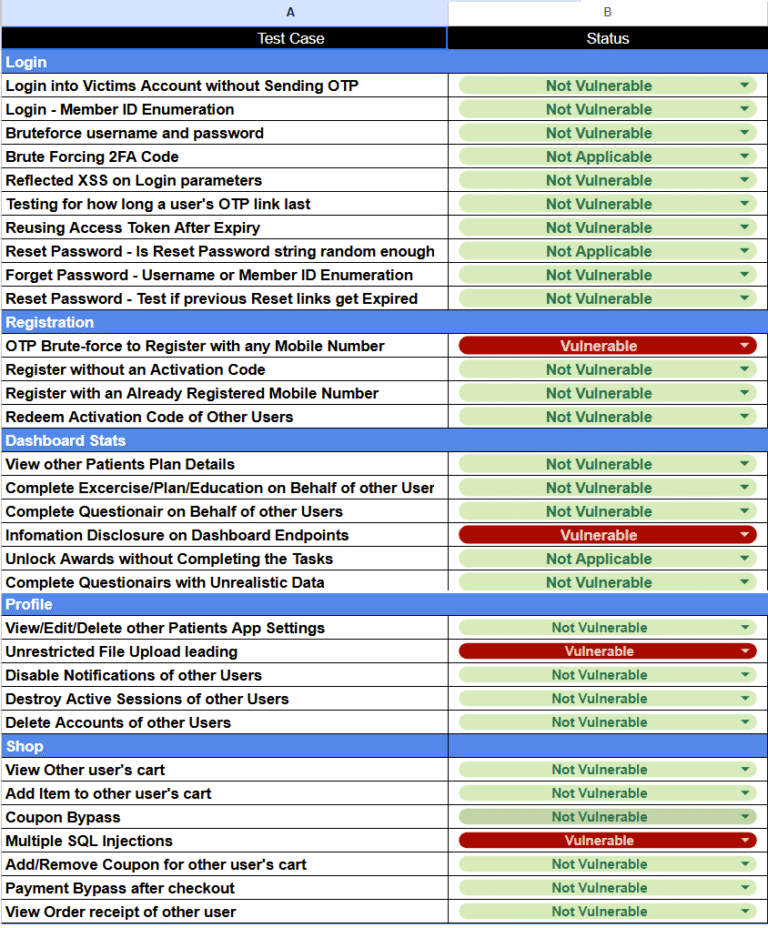
Live tracking Sheet is maintained detailing all testcases executed

Why Choose Us

Experience across sectors

We have partnered with organisations across critical sectors, including finance, education, e-commerce, and healthcare, to enhance their security posture, meet compliance requirements, and confidently pass audits.

Findings backed by evidence

We've identified critical vulnerabilities in 70% of tested applications, including server compromises and leaked credentials, and helped secure their applications and infrastructure.

Critical issues found
70%
Organisations Protected
100+
Client Satisfaction Rate
98%

Plan for Web Pentest

Web Application Pentest Plan
Web Application Security Assessment

Pentest Test Type

Methodology

Web Pentest/ API

1. OWASP Testing Guide(WSTG) and OWASP API Security Project.

2. Manual Effort: Essential to identify logical flaws, chaining of value

Mobile Pentest

1. OWASP Testing Guide(WSTG) and OWASP API Security Project.

2. Manual Effort: Critical to inspect local storge, perform code and binary analysis, bypass root/jailbreak checks, and manipulate traffics

Network Pentest

1. PTES(Penetration Testing Execution Standard)

2. NIST SP 800-115

3. Manual Effort: Verification is needed for exploit validation, chaining vulnerabilities, false positive reduction, and lateral movement testing

OWASP ZAP, wfuzz, Ffuf, Gobuster, Nikto, SQLMap, SubList3r, Wappalyzer, Google Hacking, BurpSuite, Custom Tools/Scripts, Metasploit, Nessus, Hydra, Nexpose, John the Ripper, CrackMapExec, Hashcat, Nmap and NSE Scripts, Wireshark, Enum4linux, Powerview, Netcat/Socat and Manual Hands-on Activity

100% Pentest Quality

Specialized Penetration Tester
  • 6+ years of hands-on experiencePenetration testing for enterprises and SMEs.
  • Industry-recognised certificationsOSCP, CREST CRT and HTB CPTS.
  • Secured 100+ applicationswith 14 five-star verified reviews.
A laptop showing application security tests beside a framed certification and an assessment report
Transparency via Live Tracking Sheet
  • Follow every test caseA live sheet documents each test case executed.
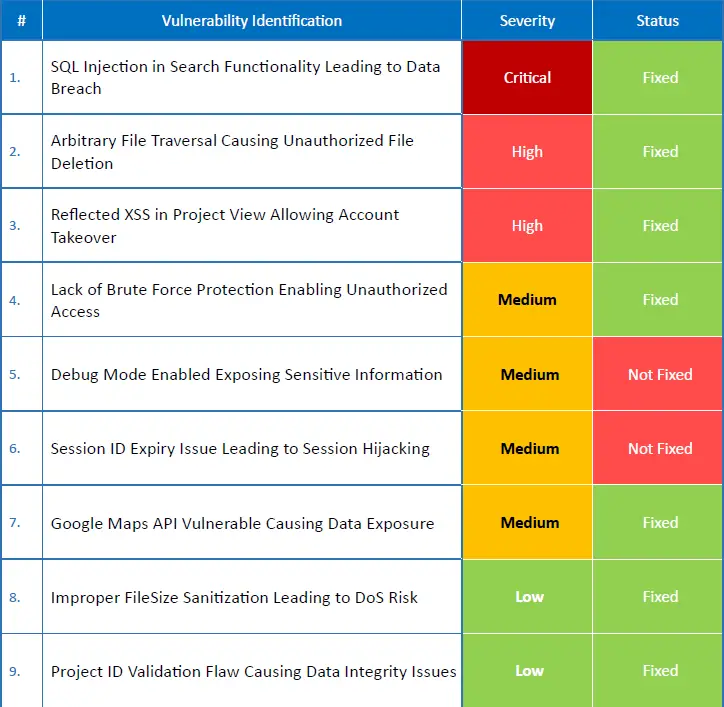
  • Track vulnerabilities in one placeFind identified vulnerabilities together in a dedicated tab.
  • Review supporting evidenceEach vulnerability has its own detailed section with evidence images.
View Live Tracking sheet example (opens in a new tab)
Example penetration testing report and evidence
In-depth Testing That Prioritises Security
  • Manual business logic testingInvestigate privilege escalation, logic bypasses and application-specific flaws.
  • Chained exploit scenariosCombine lower-risk issues to establish their real impact.
  • Comprehensive role-based testingValidate permission boundaries across every user role.
Network testing evidence
Impactful Findings, No False Positives
  • Validated vulnerabilitiesConfirm exploitation before a finding enters your report.
  • Clear evidence of impactDocument findings with screenshots and reproducible steps.
  • Practical remediation supportDemonstrate findings to your developers so they can prioritise fixes.
Documented application security findings

Pentest Report

1- Executive Summary

High Level summary and Business risk impact

3- Scope of Engagement

Sets clear boundaries and expectations

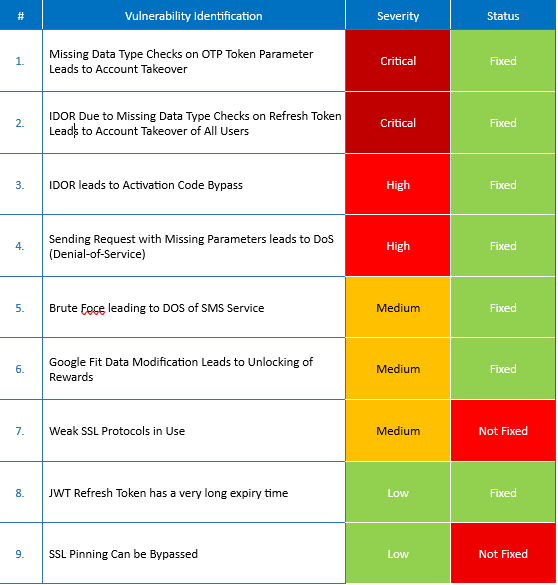
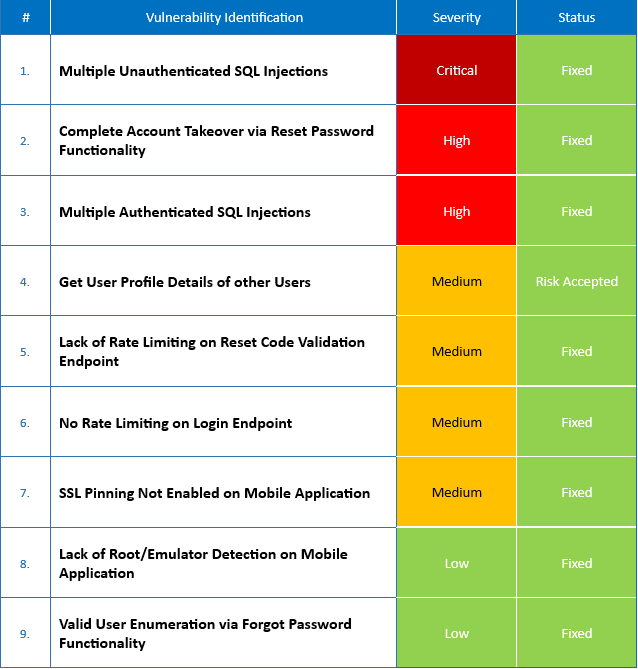
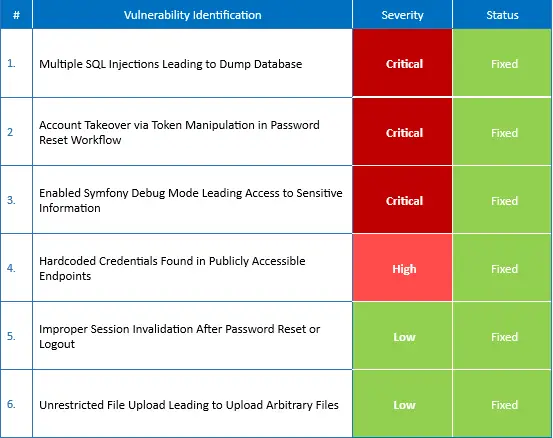
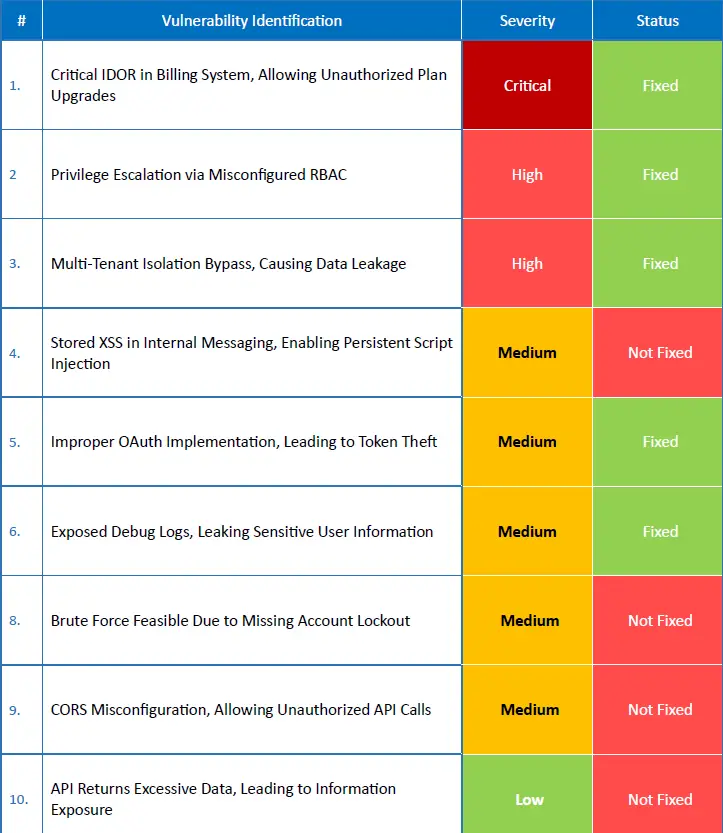
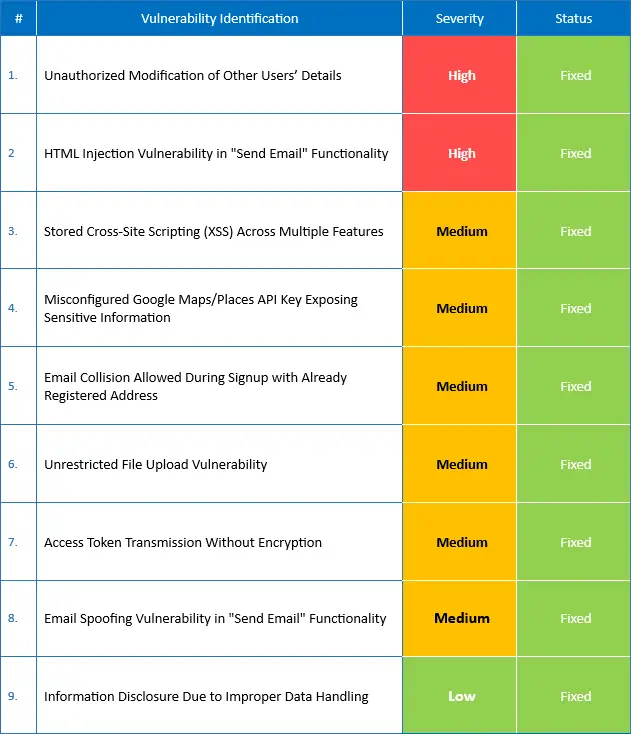
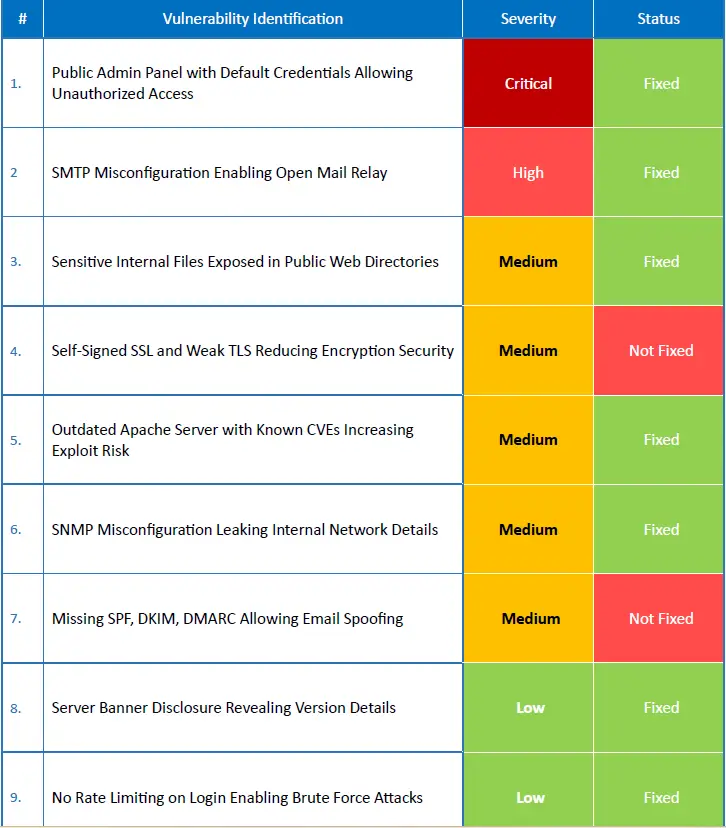
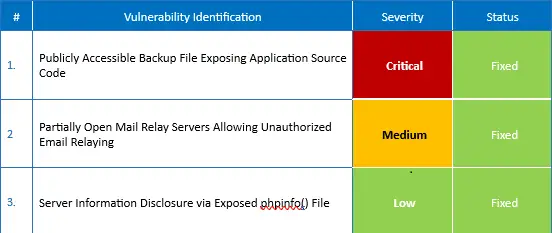
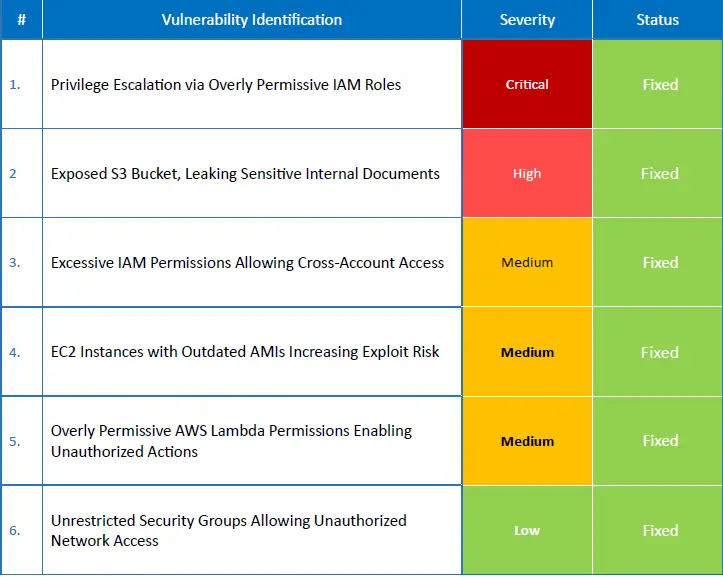
5- Finding Summary Table

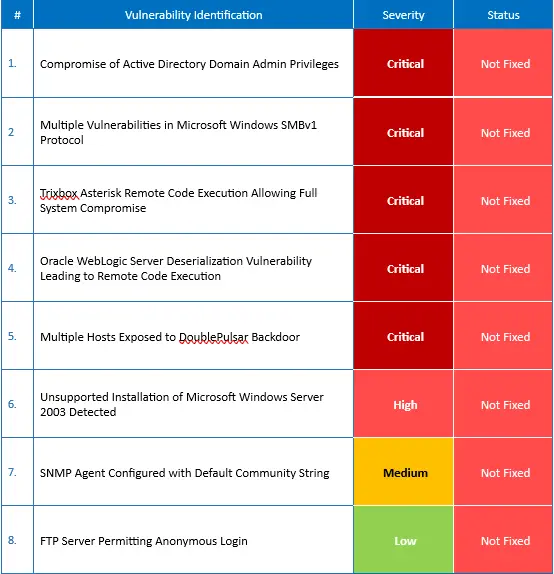
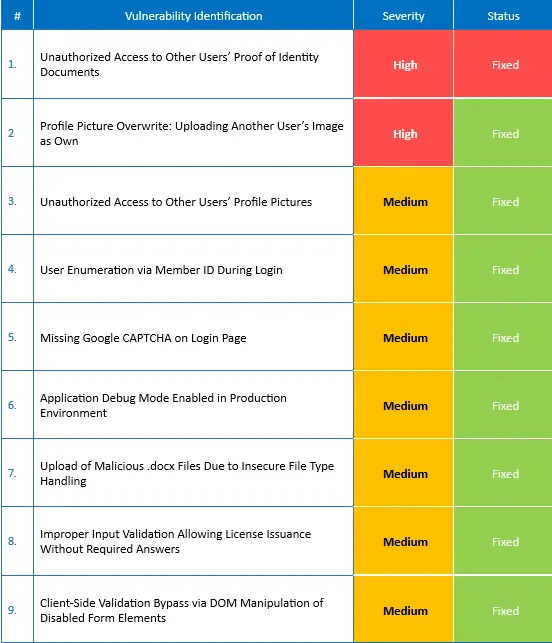
Includes vulnerability titles, CVSS v3.1 severity ratings and remediation status

Sample penetration testing report

Loading report…

Open PDF
2- Detailed Findings

Title, Severity, Asset affected, Description, Impact, Remediation guidance, References, Evidence Images

4- Conclusion and Attestation

Summary of findings and security posture and formal confirmation of pentest execution

Case Studies

Our Clients

Michael Wendland
Michael WendlandPartner at Bonsai

Reliable and professional penetration testing partner

5 out of 5 stars

"Penva Security provided a quick and efficient pentest report that satisfied our needs and certification criteria. I would highly recommend them for penetration testing, and will be using their services again in the future."

Answers to Key Questions

Why two types of Pricing

To align with market demand and budget constraints, We’ve introduced tailored packages for clients primarily seeking pentest PDF reports without a detailed security focus.

  • The cost of penetration testing in Australia varies based on factors like the scope of the test, complexity of systems, type of testing (web, mobile, network, cloud), and compliance requirements. Larger environments or ongoing testing packages typically cost more. Certified testers using advanced tools and methodologies provide detailed reports that add value by improving security and meeting regulatory standards.


Here’s a simple and concise explanation of the pentest methodology in numbered steps:

 
  1. Planning and Scope Definition: Define test objectives, target systems, and agree on a detailed quotation with the client to set clear expectations.

  2. Execution of Penetration Test: Use certified penetration testing tools and manual techniques to gather information, identify vulnerabilities, and simulate real-world cyberattacks to exploit weaknesses.

  3. Reporting: Deliver a comprehensive penetration testing report that highlights discovered security flaws, risk ratings, and actionable remediation recommendations.

  4. Remediation and Retesting: Collaborate with the client to fix vulnerabilities and perform retesting to confirm the effectiveness of security controls.


Our penetration testing is conducted by OSCP and CREST-certified experts, and our reports are globally recognized and trusted by regulatory bodies and stakeholders.

Please don’t hesitate to contact us and ask for the certifications to verify.

  • Automated scanners are typically limited in detecting complex vulnerabilities. Our team performs a detailed, and comprehensive manual penetration test, leveraging industry standards such as the OWASP Top 10, to provide a deeper, more accurate security assessment.

     
  • CREST certification is a globally recognized standard for penetration testers, ensuring professionals meet precise industry requirements. It matters because CREST is partnered with governments, regulators, and industry leaders, making it a trusted certification for high-quality, reliable security testing, demonstrating compliance with international standards.


Some of the clients worked with us on Upwork. We have maintained a 100% satisfaction rating on Upwork.

You can explore our reviews and see feedback from past clients.

Get In Touch

Book a scoping call

Choose a time that works for you.

30 min

Tell us what you need

Share your scope, priorities and deadline.

Share your scope and we'll help you plan the next step.

A clear next step

We'll review your requirements with you and confirm the scope before testing begins.

Prefer to get in touch directly? contact@penvasecurity.com.au